

Florida organizations deserve someone to help them own the whole picture.
One advisory practice across six governance domains. We meet you where you are, build a roadmap designed to function as one system, and work the gaps in the order that fits your organization.
Request a briefingThe same six domains. A different conversation in each sector.
Select where you sit today.
Preparation windows are longer than compliance windows.
Health systems, physician groups, and post-acute providers preparing for what is coming rather than reacting to it.
Obligations sit across privacy, security, vendor risk, and now clinical AI, usually under separate owners working separate calendars.
The organizations in the least difficulty later tend to be the ones that built the inventory and the cadence before they were asked to produce them.
Each sector arrives with a different starting point. The first conversation is how we find yours.
Request a briefingFragmented oversight is the real exposure.
Security is reactive.
Work is triggered by incidents, audits, and renewals rather than by a cycle the organization sets for itself.
AI initiatives move ahead of policy.
Tools arrive through departments and vendors and enter daily use before anyone has defined approved use.
Compliance functions operate in silos.
The same evidence is gathered more than once, in different formats, for different audiences.
Boards receive inconsistent risk narratives.
Each report reflects whoever prepared it, so trend and priority are difficult to read across meetings.
Devensa integrates these functions into one executive model. We do not add complexity. We design operating architecture.
What each domain is actually for.
Governance, compliance, and risk read as cost and process to most leadership teams. Stated as outcomes, they are terms leadership already cares about. Work one domain at a time and close its gaps, or run several in parallel. Each one closes into the same structure.
Continuity
Service keeps running through the week that would otherwise have stopped it. Recovery is a plan, not an improvisation.
- Security program charter, ownership, and executive reporting cadence
- Control framework selection and security architecture review
- Incident response structure, playbooks, and tabletop exercises
Permission to move
Staff can adopt new tools because the rails already exist. Policy stops arriving after the tools do.
- Use case inventory and risk tiering across the organization
- Acceptable use policy, human oversight, and escalation paths
- Model and vendor review requirements before adoption
One narrative
The board or commission hears the same risk story each time it meets, with the same measures behind it.
- Risk register design with named owners and review intervals
- Risk appetite, tolerance thresholds, and escalation criteria
- A consistent reporting format for boards and commissions
Defensibility
When an auditor, an insurer, or a funding agency asks, the answer is documented, current, and owned.
- Obligation mapping across statute, contract, and funding conditions
- Internal control design and routine evidence collection
- Audit readiness and a structure for remediating findings
Public trust
Residents, patients, and students can see how their information is held and who is answerable for it.
- Personal data inventory and records of processing
- Notice, consent, and individual rights procedures
- Third party and processor oversight, from intake to exit
Capacity
Data becomes something departments can build on rather than something nobody wants to own.
- Data ownership and stewardship model across departments
- Classification, retention, and quality standards
- A modernization roadmap for platforms and reporting
We meet each client where they are and build a roadmap that is designed to function as one system for improved maturity. That integration is the difference.
A sequence you can start, pause, and resume at your speed and budget.
Educate
Build executive and workforce understanding of value, limits, threats, and approved use.
Assess
Inventory use cases and systems. Evaluate data, identity, integrations, and third-party exposure, then score maturity in each domain.
Plan
Sequence the gaps into a roadmap with owners, budget, and a defined order of work.
Execute
Work the roadmap in sequence: controls, policy, and testing, with monitoring and response playbooks behind them.
Govern
Hold attestation-ready evidence, review cadence, and reporting so the structure stays in place.
Scored on TruMaturity™
Assessment is scored on the proprietary TruMaturity™ framework, which produces a maturity score for each domain and an overall TruMaturity™ score. Those scores are structured to guide budget allocation discussions and to prioritize which gaps are addressed first.
Built for a budget cycle
The sequence is designed to fit how public bodies actually fund work: one domain at a time, with a scored before and after, so each request carries its own justification and each completed step raises the same overall measure.
How Devensa Advisory compares with the alternatives.
Four common ways to close a governance gap, compared side by side on what each covers and what remains once the work ends. Only one covers all six domains on a single scale.
Hire the function
Depth in one domain, on one salary line.
The role, for as long as the person stays.
Retain a project consultant
Expert judgment inside a defined scope.
A report, and the question of who operates it.
Buy a tool
The loudest problem, addressed directly.
A tool to administer, and five domains unmeasured.
Devensa Advisory
All six domains, scored on one scale.
Measurable maturity across all six domains, and the structure your own team runs to hold it.
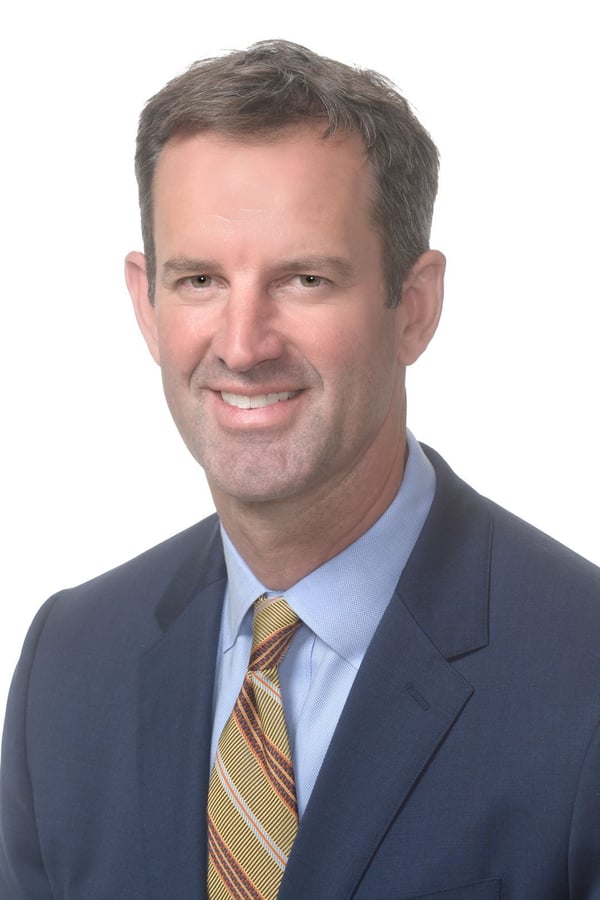
Bryan J. Langley
Executive Advisor, Critical Infrastructure, Devensa Advisory
LinkedIn profileBryan J. Langley spent his career at the intersection of public safety, critical infrastructure, and government leadership before joining Devensa Advisory as Executive Advisor, Critical Infrastructure.
He was appointed Senior Advisor at Cyber Florida, where he led and coordinated public and private efforts to develop the state’s critical infrastructure risk assessment, including a report to the Governor, the Legislature, and the Cybersecurity Advisory Council on protecting Florida’s critical infrastructure from major cybersecurity incidents.
He served as Senior Vice President of Defense Development at the Indiana Economic Development Corporation, building the state’s long-term investment strategy in the defense sector. Before that, he was Executive Director of the Indiana Department of Homeland Security and the state’s Homeland Security Advisor to the U.S. Department of Homeland Security, overseeing the State Fire Marshal’s Office, Emergency Management, and the State Building Commissioner, and chairing Indiana’s School Safety and Cybersecurity boards.
His background also includes global security leadership at Cummins Inc., consulting at Booz Allen Hamilton, and service in the White House as U.S. Assistant Chief of Protocol under the George W. Bush administration.
What is already in writing.
Section 282.3185, Florida Statutes
Counties and municipalities are required to adopt NIST-aligned cybersecurity standards, provide tiered employee training, and report incidents on defined timelines.
America’s Water Infrastructure Act, Section 2013
Community water systems above a defined population threshold are required to assess risk and resilience, including the security of the automated systems they operate, and recertify every five years.
HIPAA Security Rule
A proposed overhaul would add mandatory risk analysis cadence, asset inventory, network mapping, and defined testing schedules. Preparation windows are longer than compliance windows.
Artificial intelligence
Florida has not adopted an AI mandate. Obligations arrive instead through duties that already exist: public records, procurement terms, privacy requirements, and contracts already signed. Adoption commonly moves ahead of the policy governing it.
The questions we are asked first.
How is this different from what our IT team already does?
It complements the work IT is already doing. IT carries the systems. Devensa works across all six domains, at the executive level and in the delivery itself, naming owners across departments, building policy and controls, and defining what gets reported and to whom. Several of those domains reach past IT into legal, procurement, operations, and clinical or field leadership, which is why the work sits above any single function.
What do you actually deliver?
A comprehensive menu across all six governance domains: program design, policy and control build, architecture and process review, testing and exercises, training, recurring review, and fractional executive leadership where it fits. Work is selected against your maturity roadmap rather than sold as a fixed package.
Are you selling a tool?
No. Devensa Advisory does not resell or implement third-party security products, and takes no position on which ones you run.
Can you work alongside the vendors and consultants we already use?
Yes. Devensa works alongside the providers already in place, and nothing here requires changing them. In most cases the engagement clarifies what each one is accountable for and where the remaining work sits.
Do we have to start with all six domains?
No. Most organizations start with one domain and add others as capacity and budget allow. Because the work in every domain is sequenced against the same maturity roadmap, each piece raises the same overall measure instead of becoming a separate program.
How does this fit a public budget cycle?
Each domain carries a scored position before and after, so a request can be justified on its own terms. The sequence is built to pause at a fiscal year boundary and resume without rework.
What does a board or commission actually see?
One risk narrative, using the same measures at every meeting, with the domain breakdown sitting behind a single overall score.
We already have an assessment on file.
Good. An assessment describes a point in time. What we look at is whether ownership, cadence, and reporting exist to carry its findings forward, and what happens to them between cycles.
Start with a conversation, not a proposal.
Devensa offers a no-fee leadership or board briefing on governance structure in your sector. No pitch, no assessment required.
- A plain description of how your six domains are governed today
- Where accountability is currently unassigned
- A sequence you can take into a budget conversation
Working with organizations across Florida, including Tampa Bay, Orlando, Jacksonville, Miami, and Tallahassee.
Interested in continuous attestation on the Devensa AI platform? Join the early access list